
When data leaks become news: The cybersecurity questions every journalist must ask
A responsible data leak investigation must verify the evidence, protect affected people and explain who failed, without republishing private information.

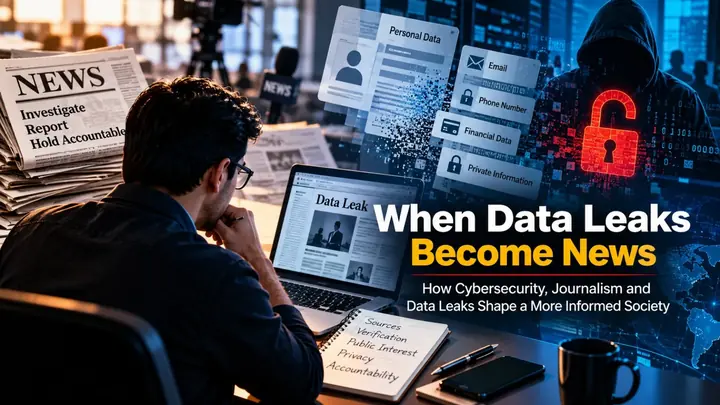
A database appears online. It contains names, phone numbers, email addresses or financial details. Screenshots begin circulating, and someone calls it a “massive breach”. For a newsroom, that is not the finish line. It is the start of a careful investigation.
Data leaks sit at the point where technology, privacy and public accountability meet. The technical failure matters, but so do the decisions that allowed it, the people put at risk and the response from the organisation responsible for the information.
A leaked file is evidence, not a ready-made story
The first task is to establish what the material actually is. A file can be genuine, partly altered, assembled from older breaches or falsely linked to a company or public agency. A large record count can also be misleading because databases often contain duplicate or outdated entries.
Before reporting, journalists should test the basic claims. When was the data collected? Does a small, safe sample match information that can be independently verified? Is the alleged owner of the database identifiable from internal fields, official statements or technical evidence? Has a cybersecurity researcher examined the material without redistributing it?
The language of the report should match the evidence. A confirmed breach, an exposed database, a claim by an anonymous seller and a set of records circulating online are different situations. Calling all of them a “hack” can mislead readers and unfairly assign blame.
The real story is accountability
The number of exposed records may attract attention, but public-interest reporting should go further. Was sensitive information stored without adequate protection? Were earlier warnings ignored? How long was the information exposed? Did the organisation notify affected people, regulators or law enforcement? What support was offered to those at risk?
Those questions move the story away from spectacle and towards responsibility. They also help readers understand whether the incident was caused by an external attack, a misconfigured server, weak access controls, an insider or another failure. A hooded attacker is a familiar visual shorthand, but many damaging leaks begin with ordinary mistakes.
Public interest does not mean publishing everything
Access to private information does not create an automatic right to publish it. A dataset may contain home addresses, identity numbers, medical records, private messages or details about people who have no connection to the misconduct being investigated.
Publishing raw files can repeat and deepen the original harm. Responsible coverage should redact unnecessary identifiers, avoid linking to downloadable databases and reveal only the material needed to prove the public-interest finding. A report can establish that security failed without turning victims’ personal information into a searchable resource.
Editors should also consider whether contacting people in a leaked dataset could expose them to further risk. Where verification is necessary, outreach should be limited, secure and transparent about how the contact information was obtained.
Protect the evidence and the source
Leaked material can carry hidden risks. Files may contain malware, tracking links or metadata that identifies a source. Newsrooms should isolate suspicious files, preserve an untouched copy, record where and when the material was received and restrict access to the smallest necessary team.
Confidential communication also needs protection. A compromised email account, an unlocked phone or a shared cloud folder can expose unpublished investigations and source identities. Strong passwords, multifactor authentication, encrypted communication where appropriate, timely software updates and reliable backups are basic reporting safeguards, not optional IT extras.
Journalists need working cyber literacy
Reporters do not need to become penetration testers. They do need enough technical understanding to ask precise questions and recognise weak claims. That includes knowing the difference between a breach and an accidental exposure, understanding the limits of metadata, preserving digital evidence and recognising common phishing or impersonation tactics.
Collaboration produces stronger work. Security specialists can explain how a system failed and what the available evidence proves. Journalists can examine governance, accountability and the human consequences. Editors and legal advisers can test whether publication serves the public interest while limiting avoidable harm.
A practical newsroom checklist
- Verify the origin, date and ownership of the data before describing the incident.
- Separate confirmed facts from claims made by anonymous sources or sellers.
- Do not publish passwords, identity numbers, financial records or raw personal datasets.
- Ask who knew about the weakness, when they knew and how they responded.
- Protect source identities, preserve original evidence and document every handling step.
- Give the affected organisation a fair opportunity to respond without revealing a source.
- Explain what affected people can do, but avoid overstating risk or promising complete protection.
Trust is the final test
A polished statement cannot repair poor security on its own, and a dramatic headline cannot replace verification. Readers need to know what happened, what the evidence proves, who may have been harmed and what should change.
The same standard applies to the newsroom. Journalism earns trust when it investigates a leak without exploiting the people inside the data. Cybersecurity has become part of source protection, evidence handling and everyday editorial judgment. That makes it a journalistic responsibility, not a specialist concern kept outside the newsroom.
Frequently asked questions
You may also like
 National
France Orders Cybersecurity Probe After Cyberattack Disrupts Refrigeration at 480 Stores
 Technology
Hong Kong Firms Lack Board-Level AI, Cybersecurity Expertise: Report
 Technology
Kochi to host India's longest-running cybersecurity conference in October 2026
 Politics
Modi outlines four-point roadmap to transform India's fintech sector
Most read
- 1
Xi Orders Urgent Rescue Efforts After Tibet Earthquake Kills 16, Injures 54
- 2
Schools Shut in Five Tamil Nadu Districts, Including Chennai, Amid Heavy Rain
- 3
Hong Kong Insurance Authority Tightens Premium Financing Oversight as Risks Emerge
- 4
Madanpur Masters Beat Firozabad Fighters by Two Runs in T-10 Opener
- 5
eMudhra Certificate: 8 weak certificates raise Internet Security concerns as browsers act
Comments
No comments yet. Be the first to comment.